
Developer Offshore research
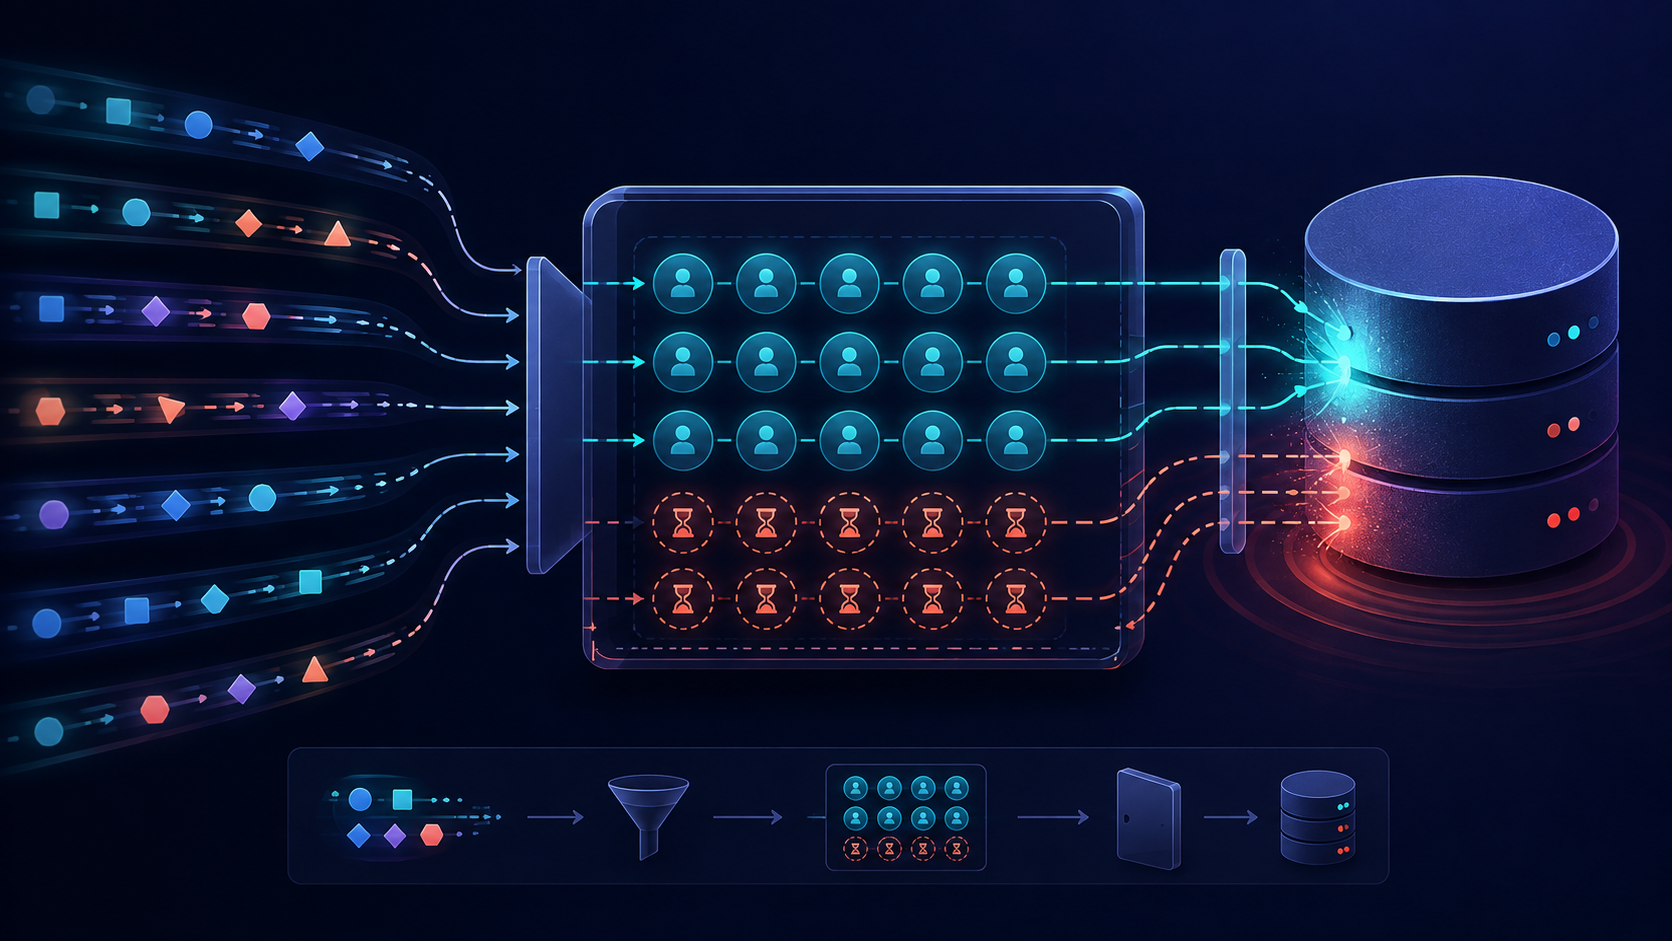
When does cache expiration create a request stampede?
· Research report
A source-backed research method for one cached key under controlled concurrent demand, separating measured behavior from inference and operational approval.
Use this report with the Research library and the related daily developer guides to turn evidence into a bounded work brief.
Key Stats
- 1 bounded unit of analysis
- 5 evidence classes compared
- 2 primary or authoritative technical references
Key Takeaways
- Measure origin requests, waiter latency, lock ownership, and stale responses.
- Challenge the result: a low average origin rate can conceal a damaging burst at expiry.
- Treat the conclusion as bounded evidence, not a universal guarantee.
Research question and scope
This report asks: When does cache expiration create a request stampede? The unit is one cached key under controlled concurrent demand, tied to a named revision, environment, workload, and observation window. It does not certify the wider platform or predict every future workload. The goal is a decision that another reviewer can reproduce.
Method
Create synthetic normal, boundary, repeated, interrupted, and recovery cases. Record origin requests, waiter latency, lock ownership, and stale responses. Preserve raw observations before interpreting them, keep time sources explicit, and rerun the nearest passing case whenever a variable changes.
What public guidance contributes
Cloudflare: Cache stampede and AWS Builders Library: Challenges with distributed systems describe relevant mechanisms and controls. They help shape the test, but they cannot prove local behavior. Only evidence from the declared system revision supports a claim about that system.
Counterevidence
Actively test the competing explanation that a low average origin rate can conceal a damaging burst at expiry. Vary concurrency, identity, timing, and failure state separately. Report disagreeing signals instead of averaging them into a reassuring headline.
Decision and ownership
A Philippines-based offshore developer can prepare fixtures, run approved comparisons, add focused instrumentation, and document a reversible correction. Internal system, security, privacy, and release owners retain sensitive access, policy exceptions, production changes, and acceptance of residual risk.
Limitations and conclusion
A controlled observation cannot cover every dependency delay, historical state, client implementation, or future traffic shape. The evidence supports only one cached key under controlled concurrent demand. State missing cases, measurement error, and the condition that would falsify the conclusion before choosing to correct, observe longer, revert, or escalate.
Evidence table
| Signal | What to inspect | Owner |
|---|---|---|
| Outcome | Acceptance evidence for the bounded task | Task reviewer |
| Control | Access, test, and approval boundary | Internal owner |
| Handoff | Open risks and next decision | Next owner |
Good distributed work is observable at the handoff: the result, evidence, limitations, and next owner are all explicit.
Frequently asked questions
Does this research establish a universal threshold?
No. It provides a reproducible method and bounded evidence for the declared unit and observation window.
Who approves production action?
The accountable internal owner approves production access, exceptions, release action, and residual risk.